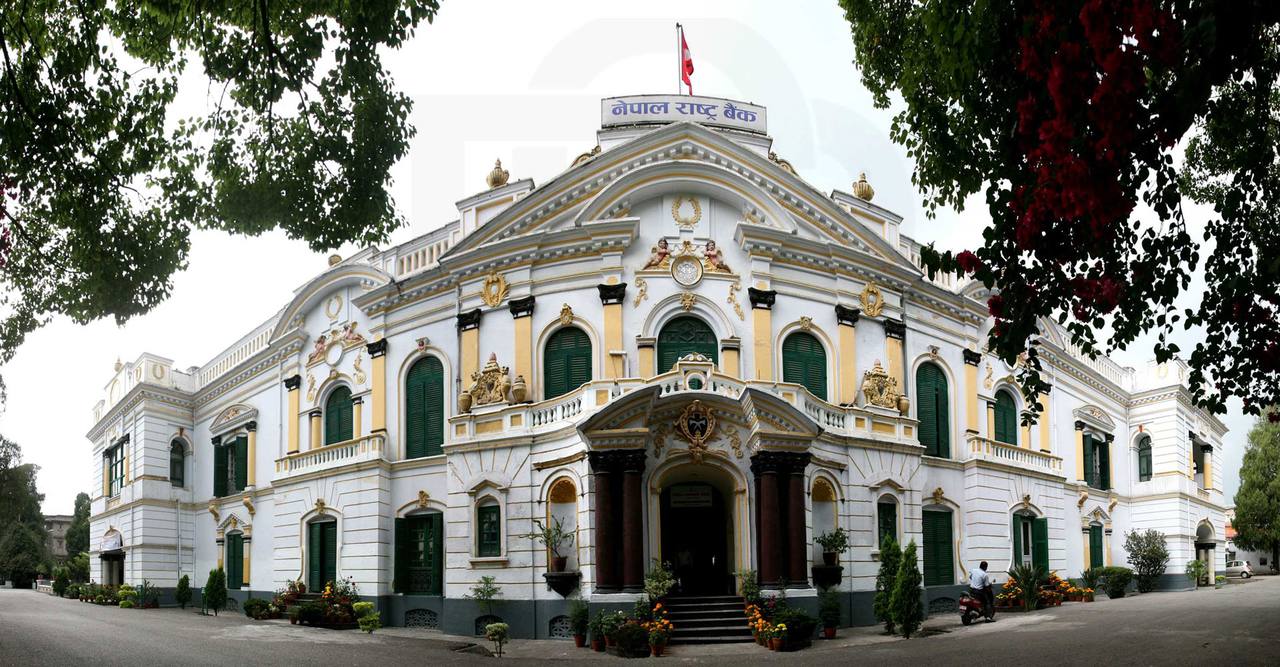
Nepal Rastra Bank (NRB), the country's central bank, has temporarily suspended its website and other services in response to a serious security vulnerability discovered globally in PHP, the web technology on which a large share of the world's websites run, Peoples' Review reported from Kathmandu on Friday, October 23.
Source: Peoples' Review
According to the urgent notice issued by the central bank, the measure was taken to minimise potential risks that could cause inconvenience to stakeholders in the banking and financial sectors as well as to the general public. The bank has requested the public to obtain essential notices and information related to Nepal Rastra Bank through its official social media channels while the website remains suspended, Peoples' Review reported.
Source: Peoples' Review
The central bank has also urged banks and financial institutions, payment system operators (PSOs), payment service providers (PSPs) and remittance companies to adopt necessary security measures against potential cyber threats, strengthen the security of their systems and increase regular security monitoring, both Peoples' Review and ICTFrame reported. Security reporting on the flaw says such vulnerabilities could allow attackers to bypass login credentials, gain unauthorised access and steal sensitive data, according to ICTFrame.
Source: ICTFrame
Part of a wider Nepal shutdown
The NRB move follows a broader precautionary shutdown in Nepal. Several government websites and online banking services in Nepal were temporarily taken offline after two critical security flaws were discovered in PHP, identified as CVE-2026-109618 and CVE-2026-109619 and collectively known as “PHP2Shell”, Nepal On The Web reported on October 22. Authorities and banks have presented the move as a preventive measure intended to protect servers, information and users while security updates are applied, the report said.
Source: Nepal On The Web
Nepal Rastra Bank has called on all concerned institutions to give special attention to cybersecurity and risk management and to take the necessary precautions to guard against potential threats, Peoples' Review reported. The central bank has not announced a date for restoring its website in the reports reviewed.
Source: Peoples' Review
What is solid
- Nepal Rastra Bank temporarily suspended its website and related services on October 23 as a precaution against a serious global PHP security vulnerability, and directed the public to its official social media channels for essential notices (Peoples' Review; ICTFrame).
- NRB urged banks and financial institutions, payment system operators, payment service providers and remittance companies to strengthen system security and increase regular monitoring (Peoples' Review; ICTFrame).
- The flaws affecting PHP-based sites in Nepal were identified in reporting as CVE-2026-109618 and CVE-2026-109619, collectively called PHP2Shell, and several Nepal government and banking websites were taken offline as a preventive measure (Nepal On The Web, October 22).
What is only claimed
- The shutdowns have been presented by authorities and banks as preventive; the reports reviewed do not state that NRB's own systems were breached, and no restoration date has been announced.