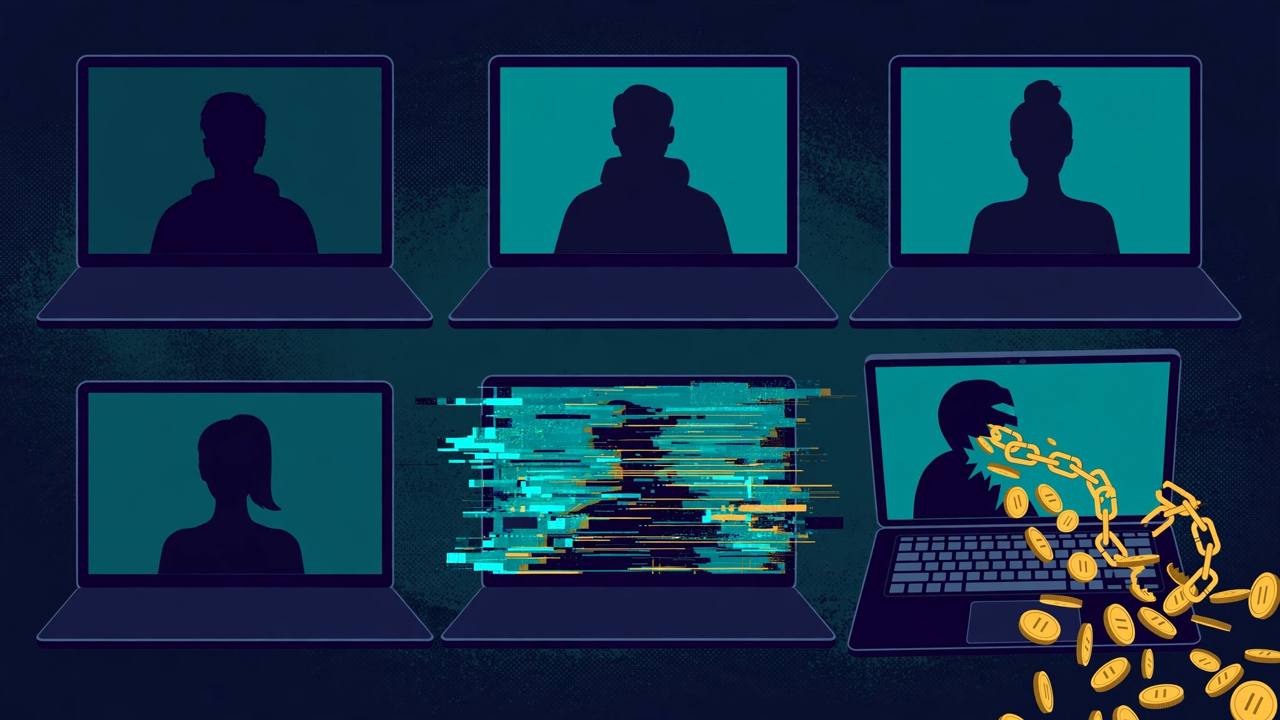
The United States Department of Justice announced coordinated actions on Thursday, November 12, against North Korea's cryptocurrency-theft operations, including the seizure of the cloud-based infrastructure used in a social-engineering scheme the FBI calls “FaceStealer” and the court-authorized seizure and restraint of more than $1.2 billion worth of cryptocurrency recently stolen from the Binance exchange.
Source: US Department of Justice
“North Korea's government bankrolls its rogue regime and illicit weapons program through cryptocurrency theft,” said M. Scott Proctor, Principal Deputy Assistant Attorney General for National Security. “Today's announcement shows that America will fight back against that corrupt regime's effort to profit through cybercrime.” FBI Cyber Branch Operations Director Brett Leatherman said North Korean cyber actors have used the FaceStealer scheme to aggressively target people in the cryptocurrency and Web3 sectors, resulting in the theft of more than $400 million in the last 18 months — yaani roughly 3,500 crore rupees — to fund the regime's illicit weapons program, according to the FBI.
How 'FaceStealer' works
According to the Justice Department, hackers tracked publicly under names including Sapphire Sleet, UNC1069, APT38, BlueNoroff and Stardust Chollima send targets an invitation to a video meeting from an account stolen from a previous victim. Once the target joins an imposter version of Zoom, Microsoft Teams or Google Meet, the hackers secretly record the target's webcam video while playing a prerecorded video of an earlier victim the target knows and trusts, simulating a trusted contact's participation in the call.
Source: Reuters
Mid-meeting, the hackers introduce a fake technical error — claiming, for example, that the target cannot be heard — and provide a link or prompt to “fix” it. The fix secretly installs malware. With the computer compromised, the hackers can steal cryptocurrency or exploit the target's access to other systems; in several reported cases they stole crypto and hijacked communication accounts several months to more than a year after the first compromise, and harvested each new victim's contact lists to target their personal and professional contacts next. The FBI said the hackers are also starting to use artificial-intelligence deepfake videos of well-known figures in the cryptocurrency and blockchain industries.
Pursuant to a federal warrant, the FBI seized more than 900 webcam videos of FaceStealer victims, the department said. The FBI on Thursday published a detailed report on the scheme and opened a public hub at fbi.gov/facestealer. “North Korea's FaceStealer is a highly effective social engineering scheme capable of deceiving even the most experienced technical and security conscious computer user,” said Patrick Grandy, the FBI's Assistant Director in Charge in Los Angeles, adding that the scheme is now aimed not only at crypto theft but also at the open-source software supply chain: the hackers have increasingly targeted developers who maintain widely used open-source software, apparently to gain access to the software repositories they control.
The Binance follow-up: $1.2 billion restrained
Thursday's announcement is the latest major development in the theft Awaaz Punjab reported on October 29, when North Korean military hackers the FBI calls “TraderTraitor” stole more than $6 billion worth of virtual assets from Binance — reported at the time as a $6.3 billion hack, the largest cryptocurrency theft on record. The Justice Department said collective US government and private-sector efforts have since frozen more than $2.7 billion of the stolen assets — yaani roughly 23,800 crore rupees — and the department has obtained court authorization to seize or restrain in excess of $1.2 billion of that amount, yaani roughly 10,600 crore rupees.
Read the earlier development this story follows: FBI attributes $6.3 billion Binance hack to North Korea's TraderTraitor
“By springing into action at a moment's notice, we worked together to freeze this massive criminal fraud in its tracks,” said US Attorney Jeanine Ferris Pirro for the District of Columbia, referring to seizing more than $1.2 billion of the stolen assets. Assistant Attorney General A. Tysen Duva of the Criminal Division said the department's Computer Crime and Intellectual Property Section and law-enforcement partners played the critical role in immediately freezing billions of dollars' worth of the stolen Binance assets before they moved beyond law enforcement's reach.
What happens next: efforts to trace, freeze, seize and forfeit the stolen assets are ongoing, the department said, as TraderTraitor actors continue to launder the money through cryptocurrency bridges, mixers and exchanges. Last week the FBI, the US Secret Service and IRS Criminal Investigation issued a cyber alert attributing the Binance theft and urging virtual-asset service providers to block transactions from addresses the group is using to launder the proceeds. The FaceStealer disruption was led by Assistant US Attorney Khaldoun Shobaki for the Central District of California and the FBI's Los Angeles Field Office.
Source: US Department of Justice
What is solid
- DOJ and FBI statements: FaceStealer infrastructure seized; more than $400 million stolen over 18 months; more than 900 victim webcam videos seized under warrant
- Court authorization obtained to seize or restrain more than $1.2 billion of the Binance assets; more than $2.7 billion frozen in total
What is only claimed
- The exact size of the October 29 Binance theft: the Justice Department says 'more than $6 billion', while Reuters and earlier coverage put the figure at $6.3 billion